Web3 scam sites constantly change their domains, branding, and visual appearance, yet their underlying logic often remains the same. The same frontend components, wallet connection flows, approval sequences, and transaction‑building mechanisms may be reused across multiple fraud campaigns.
In this talk, Dinmukhammed will demonstrate how preserved JavaScript bundles and other frontend artifacts can be analyzed even after a website has been blocked or gone offline. He will also show how wallet UX patterns can be compared across different scam sites and complemented with lightweight on‑chain verification. This approach treats scam interfaces as a reusable production layer, enabling campaign clustering, threat hunting, and defensive detection
SPEAKERS
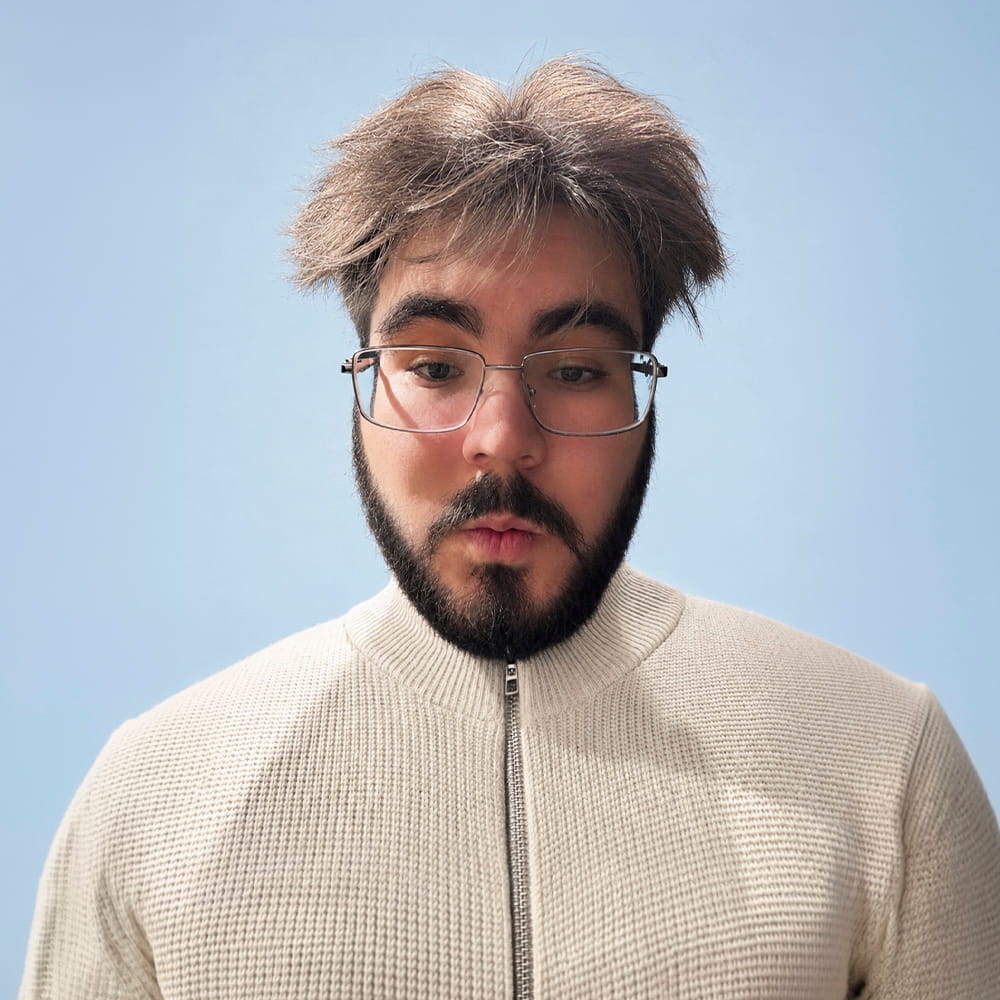
Dinmukhammed Kabiden
Independent Web3 security researcher
Dinmukhammed Kabiden is an independent Web3 security researcher specializing in threat intelligence, blockchain investigations, and phishing research. His work focuses on Web3 fraud, malicious infrastructure, on‑chain and off‑chain attribution, and identifying technical relationships between seemingly unrelated campaigns.
His research combines OSINT, frontend artifact analysis, threat intelligence, and blockchain transaction tracing. He is particularly interested in how scam operations scale through the reuse of infrastructure, code, and wallet interaction patterns

