Bug bounty has changed dramatically over the past year. AI is now used everywhere, and you cannot afford to ignore it. This is an essential tool in every security researcher’s arsenal. However, it needs to be used correctly.
The speakers have been using AI on a daily basis for over six months and would like to share the key problems they encountered and how they solved them
SPEAKERS
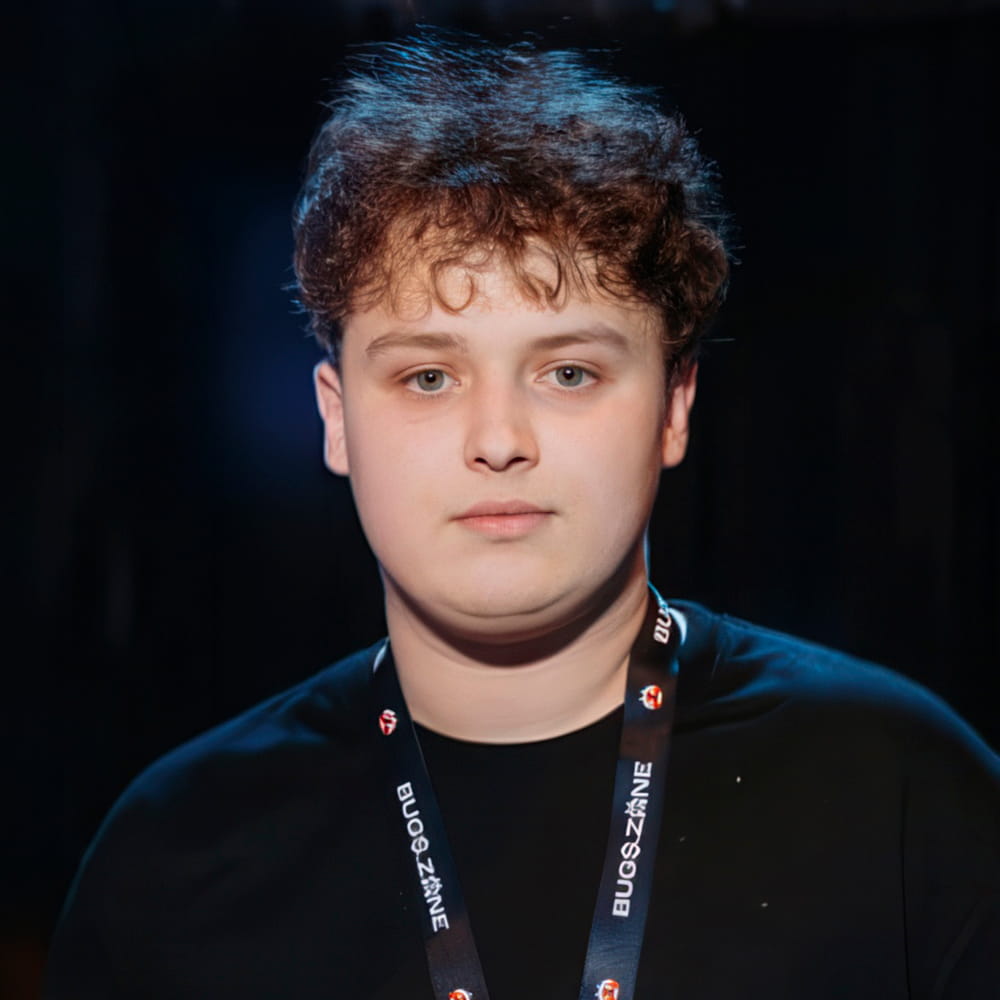
Vladislav Bek
Incident Response Specialist, Bastion
In his current role, Vladislav is responsible for incident response and investigation.
During his spare time, he hunts for vulnerabilities on the BI.ZONE Bug Bounty and Standoff 365 platforms.
Winner of BUGS ZONE 7.0 (by BI.ZONE), he participates in and organizes major Russian CTF competitions.
He runs a Telegram channel and writes articles for Habr
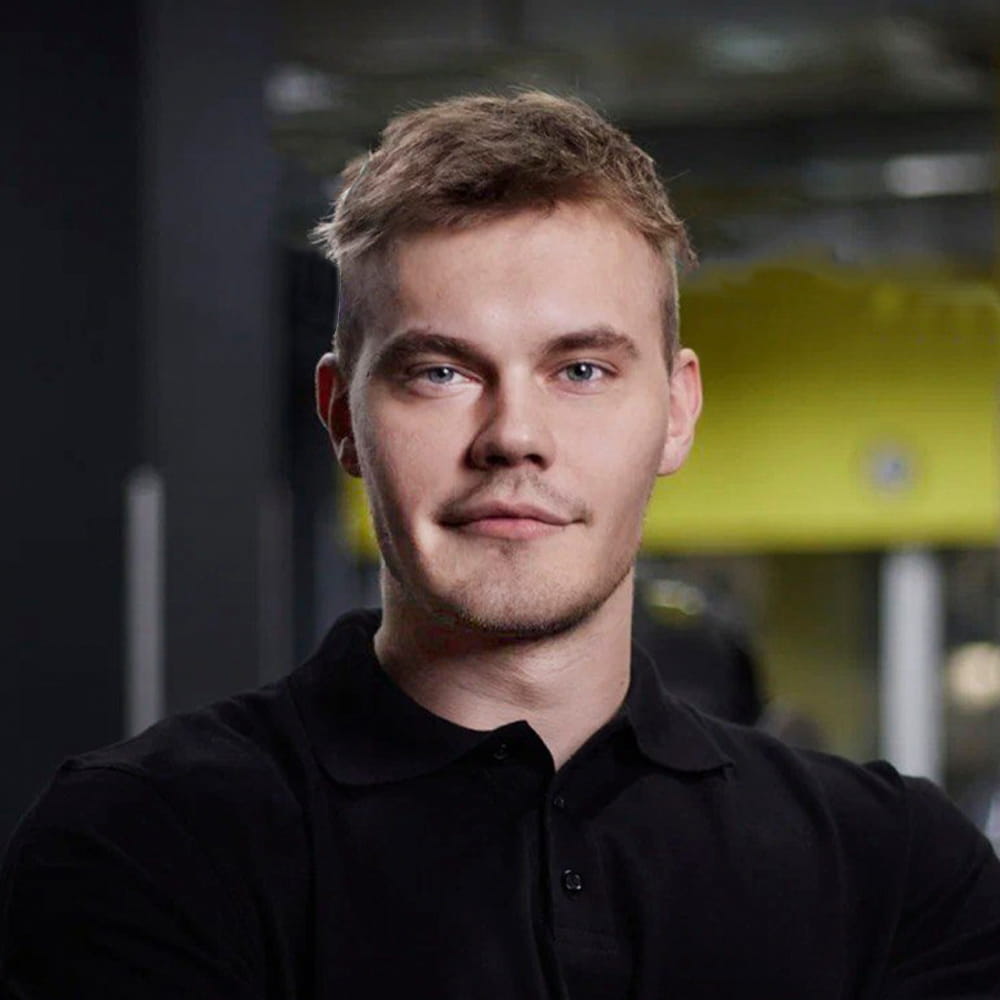
Daniil Shushakov
Penetration Tester, Jet Infosystems
Daniil began his journey with self‑development, supported by the well‑known bug hunter Ivan “rolegiv.”
Over the past year, he worked in the banking sector with a purple team. However, bug bounty was where he truly poured his heart and soul. This dedication paid off, bringing him success and top positions on the bug bounty leaderboards. He ranked first on BI.ZONE Bug Bounty last quarter.
Recently, Daniil has moved to InfoSystems as a pentester

